Sovereign by design
Platform hosted on AWS Australia with Australian-based analysts and IRAP-assessed tools. Data, staff and playbooks stay onshore, subject only to Australian law.
Sovereign Australian XDR powered by 18 global SOCs, AWS Australia hosting and 24x7 human-checked response.
Vectra Managed XDR runs on the Ensign InfoSecurity global SOC network - 18 24x7 SOCs - paired with a sovereign Australian data plane on AWS Australia. All telemetry, playbooks and staff stay onshore, subject only to Australian law. AI-driven triage and SOAR playbooks cut dwell time. A human analyst still makes the call on every escalation. The platform is vendor-agnostic. We work on your existing EDR, SIEM and cloud stack, or stand one up and run it for you as a single vendor.
Many organisations rely on Microsoft 365, so Microsoft Sentinel is the obvious choice of SIEM. Running it well is the hard part. Compliance needs, lack of time, skills gaps and no spare staff make it slow and costly to build in-house, whether you work from risk or from compliance.
Our SOC in Australia runs Sentinel for you as a full service. If it is already set up, we take it over. If not, we help you design and build it first. It covers assets on-premises, in the cloud or both.
Sentinel helps with insider threats, user behaviour, critical data protection, advanced and persistent threats, cloud security, incident response, compliance, and risk and vulnerabilities.
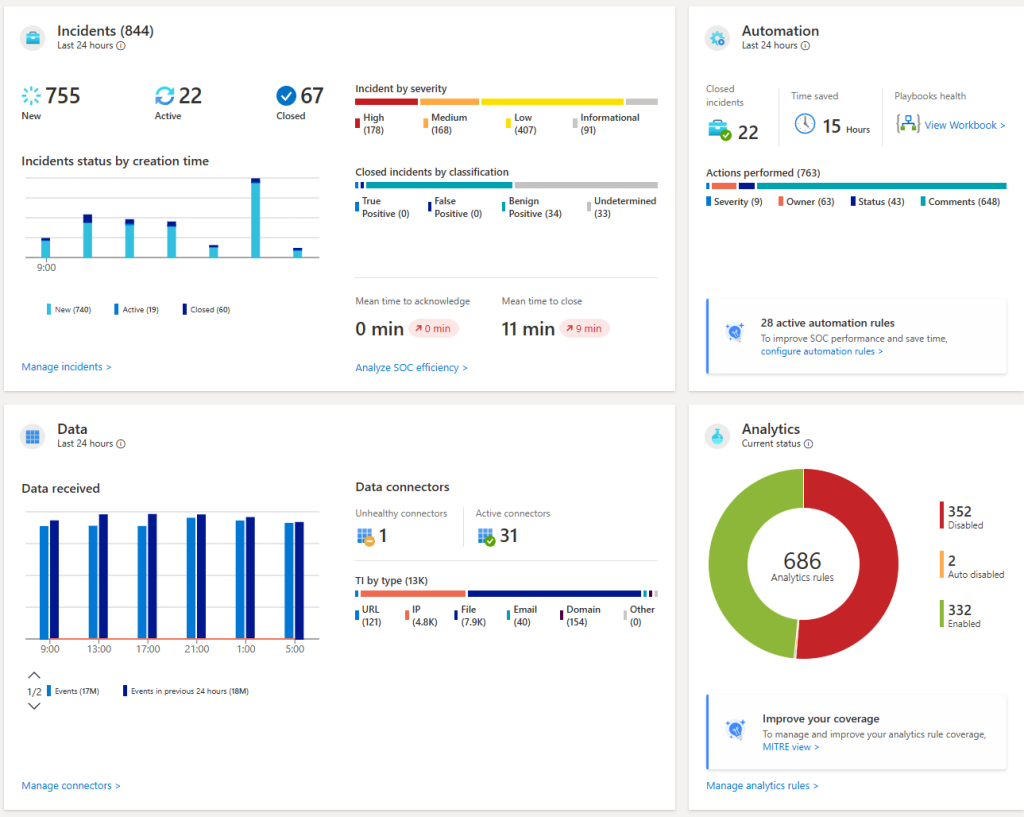
One service, kept up to date for the latest threats, so you can get on with your business.
Log collection across all users, devices and infrastructure, on-premises and multi-cloud
Daily checks, triage, watch and response, using Sentinel and curated threat intel
Threat detection, with false positives tuned out and the platform tuned daily
AI-assisted investigation and hunting for suspect activity
Real-time response and escalation, through a Microsoft Teams channel
Local threat intelligence feeds (ASD/ACSC)
External connectors and integration, plus Security Orchestration, Automation and Response (SOAR)
Vulnerability scanning and management, with clear remediation advice
A monthly security report for your team, managers and board
Expert advice, and skills passed on to your team
Platform hosted on AWS Australia with Australian-based analysts and IRAP-assessed tools. Data, staff and playbooks stay onshore, subject only to Australian law.
Built-in detection from Qualys, Tenable, Check Point, CrowdStrike and the wider tier-one vendor mesh. You're never locked into one vendor.
Part of Ensign InfoSecurity, APAC's largest pure-play cybersecurity firm. Threat intel from 18 global SOCs, applied to your Australian estate.
A per-asset monthly rate covers people, platform, playbooks and escalation. No per-alert metering, no surprise licence bills, no surge fees.
A vendor-neutral pipeline normalises EDR, identity, cloud, network and SaaS logs into a single sovereign data plane.
24x7 behavioural analytics compare your baseline with Ensign global threat intel from 18 SOCs.
Pre-approved SOAR playbooks contain in minutes. Every escalation is named, tracked and logged.
Monthly detection review, quarterly threat-model refresh, annual red-team assumption test. The baseline never stays still.
24x7 visibility across endpoint, identity, cloud and network telemetry. Combined in one platform by one team.
Managed Sentinel, Splunk, Chronicle, Elastic or DEVO. We own the platform, content, tuning and workflow. You own the value.
We normalise data, cut noise and tune detection rules against your baseline - not a generic ruleset.
Automated triage and response playbooks cut mean time to resolve. Hours become minutes.
Analyst-checked alerts with full context, an evidence chain and a suggested containment action ready for approval.
Audit trails, evidence packs and executive summaries. Aligned to APRA CPS 234, SOCI Act, IRAP and Essential Eight.
Every escalation reaches a named analyst. No auto-closed tickets. No "possible threat" verdicts. No dashboard-only products.
DEVO SIEM compares behavioural baselines with global threat intel. It finds anomalies signature-based tools miss.
Pre-approved playbooks isolate hosts, revoke sessions and quarantine identities within minutes. Once confirmed.
Flat escalation model. Your team speaks directly to the analyst working the incident, not tier-one triage staff.
Analysts check every alert as it happens, and pre-approved playbooks contain threats quickly.
Monthly business-context reports for execs, weekly detection-tuning reports for engineers. Ready for APRA, SOCI, IRAP.
Fast, analyst-checked detection of the threats your environment faces
Analyst-checked escalations with full context, an evidence chain and a suggested containment action.
Containment playbooks run from the portal. Full audit trail for APRA CPS 234, SOCI Act and Essential Eight reporting
Direct-line escalation to the senior IR team, with no call-tree and no tier-one screening.
Sovereign data plane on AWS Australia. Telemetry never leaves the jurisdiction
Both. We work with any platform - CrowdStrike, Microsoft Sentinel, SentinelOne, Splunk, Chronicle, Elastic or DEVO. If you don't have a stack yet, we'll recommend one that fits your needs and budget.
Adelaide, Sydney, Melbourne, Perth and Brisbane, part of an 18-SOC global Ensign footprint. All Australian citizens, all background-checked, and clearable to AGSVA Baseline or higher on request.
Yes. The SIEM data plane sits inside AWS Australia (ap-southeast-2 / ap-southeast-4). Telemetry, playbooks and staff remain onshore, subject only to Australian law.
Four to six weeks for a full go-live, with rolling detection coverage. We can stand up emergency monitoring in 72 hours for active incidents.
Per-asset monthly pricing gives you a steady run rate, plus a one-time onboarding engagement. We don't meter per-alert or per-incident - that rewards the wrong behaviour.
Plenty of customers run hybrid. We handle 24x7 coverage and off-hours response. Your team owns business-hours investigations and detection work. Named IR escalation still reaches the shared queue.
Containment starts within minutes via SOAR. A named senior analyst leads the investigation. Full forensic capture, cleanup and a written post-incident review are included - not just a status update.
Speak to us about your cyber governance and compliance requirements.
Message sent
A member of our team will be in touch soon at . You can also reach us during business hours on 1800 816 044.
Need us sooner? Call +61 8 8208 0800, or the 24/7 incident line on 1800 816 044 if something is happening now.