Application whitelisting
Control which software can run, so unauthorised programs can’t.
Reach Maturity Level 3 across the ACSC's eight prioritised mitigation strategies.
The Essential Eight is the Australian Signals Directorate's baseline for defending against targeted cyber attacks. We assess where you stand now, build a prioritised roadmap, and deploy controls to reach Maturity Level 1 to 3. The goal isn't a compliance tick-box. It's real resilience against the threats the Essential Eight was written to stop.
The Australian Signals Directorate’s Australian Cyber Security Centre (ACSC) publishes the Strategies to Mitigate Cyber Security Incidents. It is a ranked list of steps. They help organisations protect their systems from many kinds of attacker.
The most important of these strategies are known as the Essential Eight.
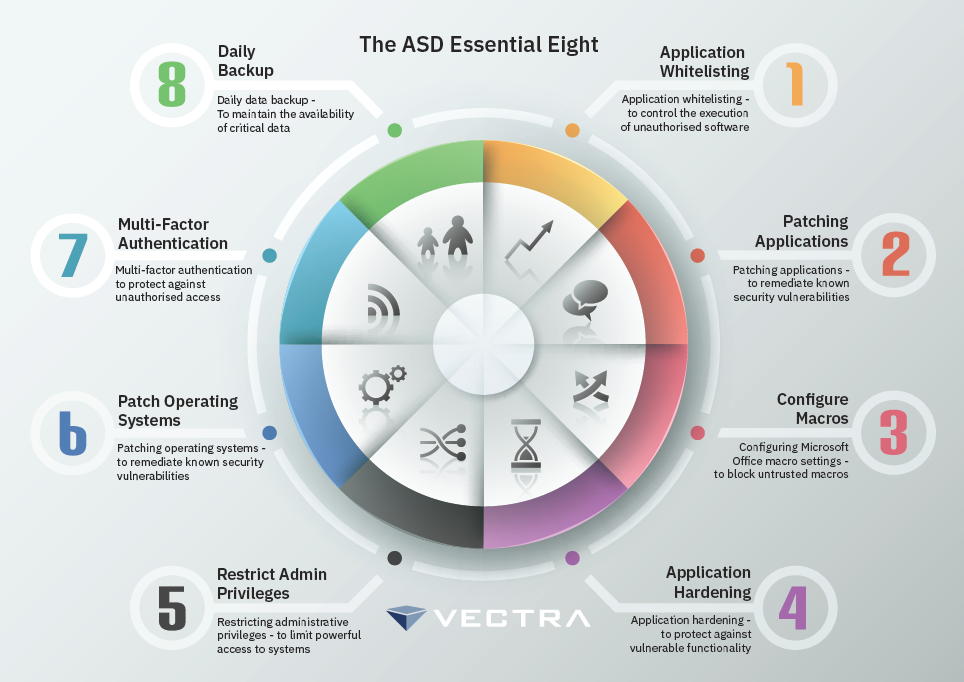
Control which software can run, so unauthorised programs can’t.
Patch apps to fix known flaws.
Set Microsoft Office macro settings to block untrusted macros.
Harden apps to protect against risky features.
Limit admin rights, so fewer people have powerful access to systems.
Patch the operating system to fix known flaws.
Use more than one proof of identity to stop unauthorised access.
Back up data every day, so key data is always there.
To help you measure how well you apply the Essential Eight, the ACSC set three maturity levels for each strategy.
As a baseline, aim for Maturity Level Three on every strategy. Vectra has the skills and people to help you get there.
Partly aligned with the intent of the strategy.
Mostly aligned with the intent of the strategy.
Fully aligned with the intent of the strategy.
Some organisations need more than Maturity Level Three.
Some are targeted again and again by skilled attackers, or work in a higher-risk setting. Where the ACSC decides an organisation needs to go beyond Maturity Level Three, it gives that organisation its own tailored advice.
We check alignment against Maturity Levels 0 to 3, across all eight mitigation strategies.
A prioritised, sequenced plan to close gaps, with effort estimates for your business, not a generic task list.
We roll out application control, patching, macro restriction, MFA, backups and all eight mitigations.
We collect evidence continuously and report to board, auditors and regulators.
An independent check on maturity claims - useful for regulated firms and supply-chain reviews.
We manage progress from ML1 to ML3 over several years: measured, reported and audit-ready.
Speak to us about your cyber governance and compliance requirements.
Message sent
A member of our team will be in touch soon at . You can also reach us during business hours on 1800 816 044.
Need us sooner? Call +61 8 8208 0800, or the 24/7 incident line on 1800 816 044 if something is happening now.