PCI DSS QSA
Australia's first PCI DSS QSA company. Full QSA delivery, from scoping and gap analysis through to ROC and AOC.
Certification programs that finish on time, at cost and survive the audit.
Vectra runs compliance certification assessments across many regulatory standards including IRAP, PCI DSS, PCI PIN, PCI SSF, PCI P2PE, ISO 27001, ISO 42001, SOC 2, Swift CSP, SOCI and CPS 234. We sit on both sides of the table - practitioners during uplift, assessors at certification. That means the controls we put in place actually meet the standard the assessor checks.
We start with a gap assessment against the framework, agree a remediation sequence, then carry the program through control design, evidence collection and the final audit. Findings are tracked in a system your team and the assessor can both see - no surprises in the closing meeting.
Managing risk is part of every business decision and of your strategy. It builds your resilience. An integrated approach to risk is not about ticking a box. It lets you take up opportunities while you respond and adapt to change and disruption.
Governance, risk and compliance (GRC) brings these three jobs together in one program.
Your activities, such as running IT operations, line up in a way that supports your business goals.
Any risk or opportunity tied to your activities is found and dealt with in a way that supports those goals. In IT, this means a full IT risk process that feeds into your enterprise risk management.
Your activities meet the laws and regulations that apply to them. In IT, this means your systems, and the data in them, are used and secured properly.
Through our partnership with SAI Global, we offer a proven, integrated suite of risk and compliance solutions. They help you manage and assess your operational and strategic risk and your compliance obligations.
If you want compliance automation instead, we also partner with Vanta. It keeps watch over your controls, gathers evidence and supports frameworks such as ISO 27001, SOC 2 and PCI DSS. We help you choose the platform that fits and set it up.
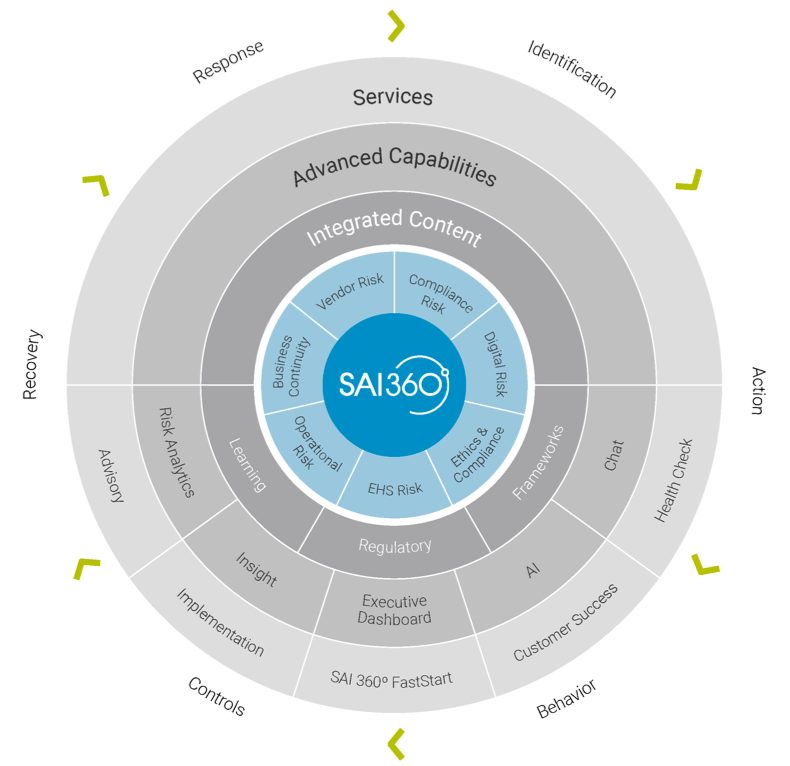
Bringing governance, risk and compliance into one approach is not easy. Done well and embedded, it gives you:
A transparent, detailed view of the risks and control environment affecting your organisation.
Streamlined processes and better engagement with the business.
Consistent communication and understanding of the risk and control environment.
The opportunity to transplant leading practices from one area to another.
Common controls shared across functions, reducing duplicated effort and investment.
Risk data aggregated easily from every part of the organisation.
The possibility of reducing the number of controls and risks.
More efficient audit plans, because audit teams can access the control and risk data.
Numerous options for improving business processes and performance.
To gain from integration, start by building a GRC strategy. It should make the financial and non-financial case, such as culture, for the investment needed to embed and sustain the program.
Internal audit, risk management and compliance must work closely together. They need to agree whether to use an existing framework, such as COSO or ISO, or adapt one to how mature your risk practice is. They also need to agree on the risk language, definitions, library of terms, governance model and the GRC platform that will support the strategy.
Questions the strategy should answer:
How should the risk functions - risk, compliance, vendor and third-party management, IT and audit - fit into one corporate framework?
How do we engage the business today, what information is it asking for, and how do we teach it about risks and controls?
How can we set up the GRC platform so it shows the risk and control picture in real time, for informed decisions?
How can we test a control once and use the result across every GRC function?
How do risks roll up, and how do they relate to each other?
What savings will we make by removing duplicate effort across the GRC functions?
What IT costs can we save by merging our GRC tools into one platform over time?
Australia's first PCI DSS QSA company. Full QSA delivery, from scoping and gap analysis through to ROC and AOC.
Assessments against the PCI PIN Security Requirements for organisations that handle cardholder PINs.
Assessments of point-to-point encryption solutions and their components against the PCI P2PE standard.
Assessments of payment software and how it is built against the PCI Software Security Framework.
Implementation, internal audit and certification support, with the same team across the lifecycle.
Alignment, readiness and certification for the new AI management system standard.
Readiness, control design and evidence for SOC 2, working alongside your auditor.
PROTECTED-certified IRAP assessors with cleared personnel, delivering against the IRAP Policy and ISM.
Assessments of information security capability against CPS 234 for APRA-regulated entities.
Independent assessments against the Swift Customer Security Controls Framework to support your yearly attestation.
Support to meet your Security of Critical Infrastructure Act obligations, including risk management programs.
Maturity uplift to ML2 and ML3, with evidence pipelines that hold up under ASD review.
A review of your people, processes and technology against good practice, with a ranked plan to close the gaps.
Speak to us about your cyber governance and compliance requirements.
Message sent
A member of our team will be in touch soon at . You can also reach us during business hours on 1800 816 044.
Need us sooner? Call +61 8 8208 0800, or the 24/7 incident line on 1800 816 044 if something is happening now.